










 FileGrant
 RemoteGrant
 Connector
 AIGrant
 EmailGrant
 SecretGrant
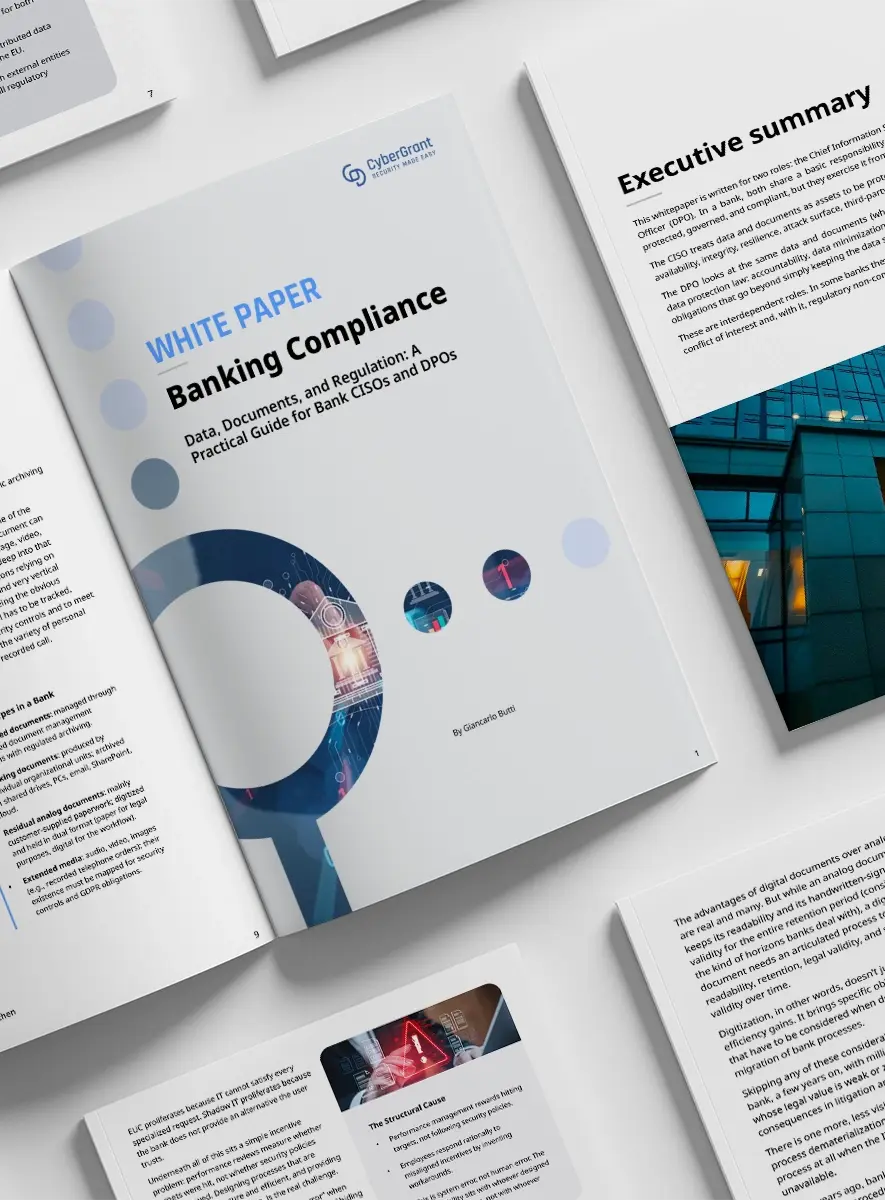
Banking Data and Documents: A Guide for CISOs and DPOs
Are your banking documents actually under control?
In banks, the share of documents outside IT control is structurally higher than senior management tends to assume: unmonitored network shares, personal PCs, personal cloud storage, unapproved AI tools. This isn't a policy failure. It's a badly designed incentive problem.
The CLUSIT 2026 Report and the Verizon DBIR 2026 point to the same picture:
- The financial sector ranks among the three most targeted industries globally
- Supply chain ICT breaches are growing steadily
- Third-party credential compromise is the most common initial access vector
- A significant share of financial sector breaches involve internal users
Stolen banking data doesn't disappear: it circulates for months or years in underground markets, sold multiple times and weaponized long after the original incident.
These aren't future scenarios. They are happening today, at institutions with the same risk structure as yours.
Download the whitepaper and discover how to govern your documents so that protection follows them wherever they go.
Banking document governance: who owns what
 CISOs and Heads of Security
Responsible for ICT risk management and document flow oversight. DORA places direct accountability on them for ICT supply chain traceability.
 CIOs, CTOs, and IT Directors
Responsible for document architecture and data governance. The whitepaper analyzes the structural gaps no existing document management system covers natively.
From data classification to the regulatory map: what the whitepaper analyzes
Why employees work around security policies even under strict controls. The analysis dismantles the human error narrative.
Email, network shares, personal PCs, personal cloud storage, generative AI tools, and third parties under GDPR Article 28.

Why stopping at confidentiality isn't enough, and what it means for the legal validity of digital documents under eIDAS 2.

From mortgage contracts to GDPR obligations: why retention is an attribute of the individual document, not the category.
Format obsolescence, electronic signatures, and operational continuity: the risks that surface too late.
Where the regulations overlap, where they complement each other, and where they create distinct obligations for CISOs and DPOs.