










 FileGrant
 RemoteGrant
 Connector
 AIGrant
 EmailGrant
 SecretGrant
Secure access, protected data
Who gets in, to what, and when: every access governed and logged, so a stolen credential never turns into an incident.
Access management: the first step to data security
Access risk is no longer the outsider forcing the door. It is the valid credential used the wrong way, the remote session opened for a vendor, the permission that stays live long after it was needed. In 2024, 90% of organizations reported at least one identity-related incident (IDSA, 2024). And once an incident hits, the problem shifts to visibility: ENISA found that in 75% of breaches the logs needed to catch the anomaly already existed, only scattered and unread (ENISA, 2026).
CyberGrant moves control from the perimeter to the data. Protection does not stop at the login: it follows the file across its entire life cycle, with role-based permissions, automatic classification, and a record of every access, inside the company and beyond it. The perimeter has already fallen, and what matters now is governing who touches the data and reconstructing what happened.
VPN and RDP under control, session by session
Remote work and outside vendors reach your systems over RDP and VPN. An open RDP port gets scanned and attacked, and one compromised third-party session becomes the entry point for lateral movement.
47% of organizations rank supply chain attacks among their top concerns (ENISA NIS360, 2026).
RemoteGrant hides the RDP port from scanners (patented technology), enforces single-user access, encrypts in-session file transfers, and controls the clipboard.
Remote access stays available, but tracked and limited to the people who are authorized.
Only what is needed, for whoever needs it, wherever the file goes
Permissions pile up over time, and manual classification cannot keep pace with the documents created every day.
The result is access that is too broad and rules that stop applying the moment a file leaves the company.
FileGrant applies granular RBAC (Admin, Contributor, Reader) and TAGs that take priority over user actions: blocking download, print, screenshot, and external sharing.
Classification runs automatically through private AI, and the rules travel with the file even outside the platform.
Credentials handled like the documents they protect
Corporate passwords move through chats, spreadsheets, and shared notes, with no expiration and no way to revoke them. InfoStealer malware grew 84% in 2024, and a valuable corporate credential sells on the dark web for 1,000 to 3,000 dollars (Clusit, 2026). With valid credentials, the attacker walks in through the front door.
SecretGrant, a FileGrant module, treats credentials like files: encryption, folders, tags, permissions, and logs. Share with an expiration date and revoke at any time without changing the password, add a second password on critical credentials, and keep a full record of who accessed what, when, and from where.
Safe even when the laptop is lost or stolen
A lost or stolen laptop exposes everything on it, if a login password is the only thing guarding it.
Data at rest, without persistent encryption, stays readable to anyone who gets hold of the disk.
RemoteGrant encrypts files transparently on the endpoint and blocks unauthorized access to them. With quantum-safe Lock&Go encryption (CRYSTALS-Kyber, NIST FIPS 203 standard, August 2024), a stolen file stays unusable, and the protection is already built for the harvest now, decrypt later logic.
Governed browsing that opens no doors to your data
Uncontrolled web access opens the way to phishing, malware, and unauthorized downloads, along with the silent upload of company files to unmanaged personal services (shadow IT).
RemoteGrant adds a secure browser with internet access control, phishing link analysis, and blocking of dangerous sites.
It stops sensitive data from being uploaded to unapproved destinations, without slowing down the people who work.
Whitepaper
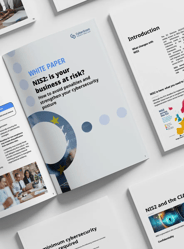
NIS2: compliance comes down to who accesses the data
Access control, audit trail, and encryption sit at the center of NIS2 obligations. The guide explains what you actually need and how to avoid the penalties.
FAQ
It is control over who can open, edit, share, or download a document, applied to the file itself and not only to the network or the login. In a file-centric model, permissions travel with the document: they stay valid even when the file leaves the company, gets forwarded, or is opened on a non-corporate device.
RemoteGrant controls RDP and VPN access session by session: it hides the RDP port from scanners, enforces single-user access, encrypts file transfers, and logs the activity. Every remote session, including a vendor's, stays tracked and contained.
Book your free demo
Talk to our security experts and learn how access control helps prevent data loss, reduce risk, and build a resilient security perimeter from endpoint to cloud