

 FileGrant
 RemoteGrant
 Connector
 AIGrant
 EmailGrant
 SecretGrant
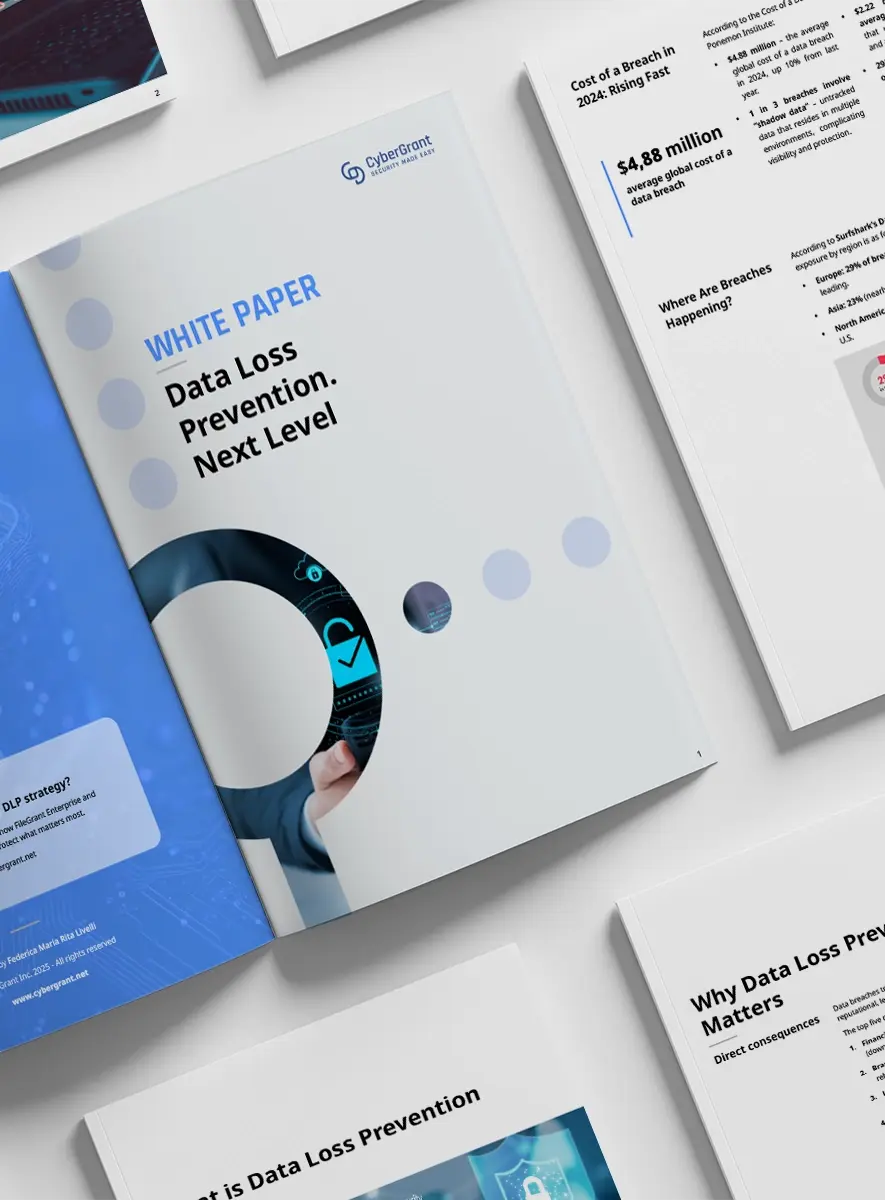
Reduce Data Leaks Caused by Human Error and Shadow IT with File-Centric DLP
- 68% of data breaches: caused by human error, phishing, or social engineering
- 15% of breaches: involve suppliers and third-party vendors in the supply chain
- 40% of attacks: exploit vulnerabilities in multi-cloud environments
Reduce Data Leaks Caused by Human Error and Shadow IT with File-Centric DLP
- 68% of data breaches: caused by human error, phishing, or social engineering
- 15% of breaches: involve suppliers and third-party vendors in the supply chain
- 40% of attacks: exploit vulnerabilities in multi-cloud environments
Who should read this CyberGrant guide
 COMPLIANCE & RISK MANAGER
Ensuring GDPR, NIS2, DORA, and ISO 27001 compliance without slowing down the business.
 IT Managers & CISOs
Reducing operational risks and managing daily security challenges with a pragmatic approach.
 Security Leaders
Looking for hands-on tools to prevent data leaks, human errors, and shadow IT.
A practical overview of risks, costs, and DLP solutions for IT Managers and Security Leaders.

Based on leading international sources: Verizon Data Breach Investigation Report, IBM-Ponemon Cost of a Data Breach Report, Surfshark Data Breach Recap, and Clusit Report 2025.

Breaches follow recurring patterns that expose structural weaknesses across organizations.

GDPR, NIS2, DORA, ISO 27001 – how a file-centric DLP supports compliance and audits while reducing costs and risks.

Healthcare, Finance, Manufacturing, and Public Sector face specific risks that demand tailored approaches.


A 5-step mini-roadmap for effective DLP, plus concrete answers with FileGrant and RemoteGrant – from file-centric control to full compliance.