

 FileGrant
 RemoteGrant
 Connector
 AIGrant
 EmailGrant
 SecretGrant
Secure and Encrypted Filesharing: a Business Imperative
Are your files really protected?
In 2025, sharing files without encryption is like leaving your safe wide open.
Modern organizations must collaborate fast, but every shared file becomes a potential entry point for increasingly aggressive attackers.
The 2025 Verizon DBIR makes it clear:
- 60% of breaches involve human error
- 30% of incidents involve third parties or external software
- 17% of attacks target industrial espionage
- 28% of financial attacks come from insiders with privileged access
The reality is harsh: credentials accidentally exposed on GitHub, confidential documents stolen by competitors, sensitive data exfiltrated by malicious insiders.
These aren’t future scenarios. They are real threats affecting companies like yours today.
Download the guide and discover how to protect your organization’s most critical data.
Secure and Encrypted Filesharing: a Business Imperative
Are your files really protected?
In 2025, sharing files without encryption is like leaving your safe wide open.
Modern organizations must collaborate fast, but every shared file becomes a potential entry point for increasingly aggressive attackers.
The 2025 Verizon DBIR makes it clear:
- 60% of breaches involve human error
- 30% of incidents involve third parties or external software
- 17% of attacks target industrial espionage
- 28% of financial attacks come from insiders with privileged access
The reality is harsh: credentials accidentally exposed on GitHub, confidential documents stolen by competitors, sensitive data exfiltrated by malicious insiders.
These aren’t future scenarios. They are real threats affecting companies like yours today.
Download the guide and discover how to protect your organization’s most critical data.
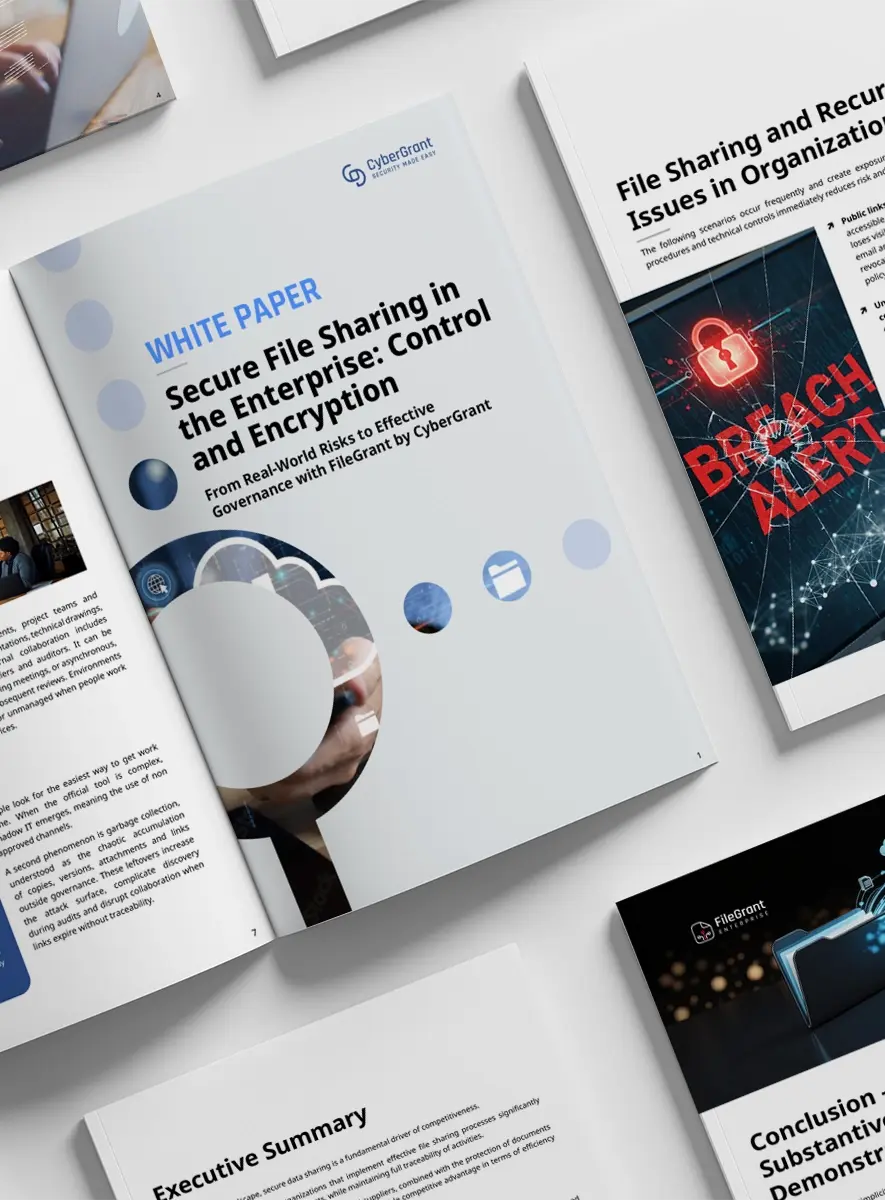
Guidelines to secure and streamline enterprise file sharing
 CIO, CISO, IT Security Managers
Responsible for technology decisions, cybersecurity controls, architecture and managing the risk created by uncontrolled file sharing.
 Risk, Compliance and DPO Teams
Ensuring data governance, accountability and alignment with GDPR, NIS2 and DORA.
 Executives and Business Owners
Assessing business impact, exposure, and investment priorities for data security.
New file sharing risks and how to control files through their lifecycle

Exfiltration techniques, AI scraping, screenshots and public links: why traditional tools are no longer enough.

Protected viewers, advanced encryption and post-download control: the trends reshaping secure filesharing.

Unapproved email, chat apps and cloud storage expose sensitive files and intellectual property outside IT’s control.

Automatic classification, anomaly detection and intelligent policy enforcement to secure the file lifecycle.

Data sovereignty, enterprise-managed keys and zero-knowledge: how to choose the most secure model for your files.

Encryption, access control, audit trails and AI-safe protections to comply with GDPR, NIS2 and DORA.